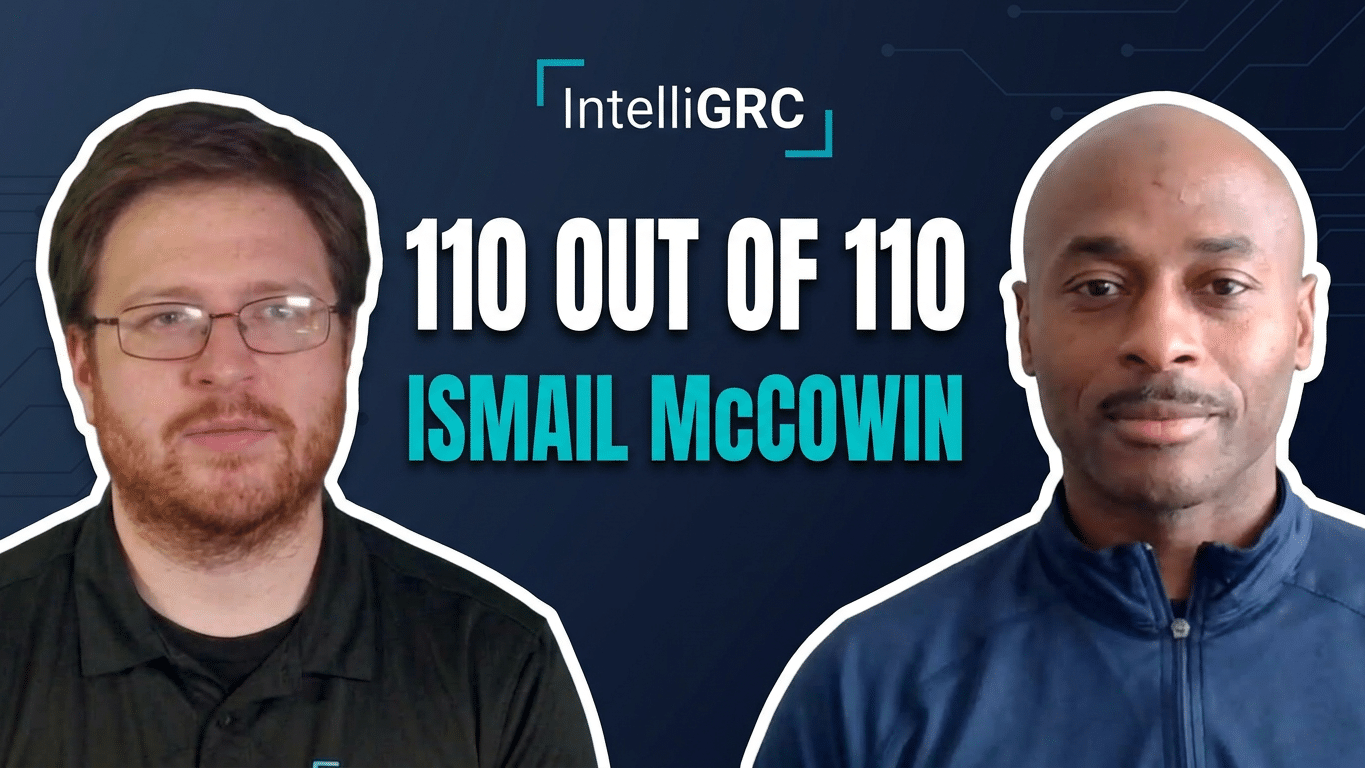
Peerless Tech Solutions passed every interview in their CMMC Level 2 assessment, then sat waiting on QA when the DoD announced the Phase 2 suspension. The certification came through anyway: 110 out of 110, zero failed controls. In Episode 20 of the IntelliGRC Podcast, Steven Molter sits down with Ismail McCowin, Director of Cybersecurity and Compliance at Peerless, to unpack why an MSP that does not process CUI chose to get certified anyway, and what the process looked like from the inside.
Ismail’s road to the DIB started in a Detroit shoe store, where a Navy recruiter walked in, bought nothing, and recruited the salesman instead. What followed was more than 26 years in cybersecurity: enlisted IT in 1997, commissioning as a Mustang officer in 2010, mission commander supporting offensive cyber operations, and deputy director of a security operations center before retiring. He brought the Navy’s readiness model of manning, training, and equipping straight into how Peerless prepares defense contractors for CMMC.
Steven and Ismail get into the requirements contractors misunderstand most, starting with identifying CUI and the “I’ve never seen CUI, so 7012 doesn’t apply to me” objection. They cover why CMMC is really a continuous monitoring program, what the pause could mean for the DoD’s next moves, and why “compliance doesn’t equal security” is only half true. If you’re an MSP or defense contractor trying to figure out your next move while Phase 2 sits in review, this one is worth your time.